System & Security (SYS)
Identity, access, and audit for the whole platform, enforced in one place rather than configured nineteen times.
Capabilities
What it does
- Role-based access control with scope overrides down to field level
- SSO, SCIM provisioning, and enforced MFA
- Immutable audit log covering every read and write
- Regional data residency and retention policies
- API tokens, webhooks, and rate controls
- Tenant isolation with per-tenant encryption keys
AI LAYER
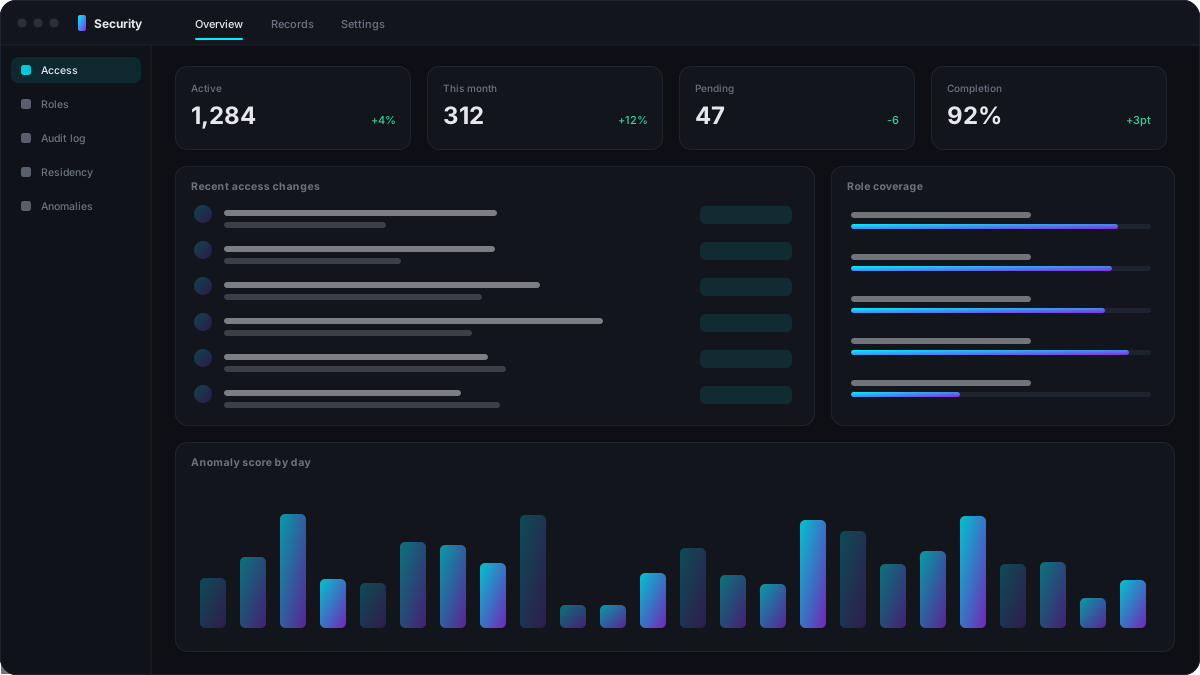
Access anomaly detection that flags permission grants outside a role's normal pattern, and compliance drift alerts when a policy stops matching the configuration underneath it.